Before looking at documents and security measures, it helps to understand what you are actually giving a vendor. Granting access and sharing data are not the same thing.
Access means the vendor can log into a system you control. Access can usually be limited or revoked quickly.
Data sharing means you give the vendor copies of files or datasets. Shared data is harder to control once it leaves your environment.
This distinction matters because each type of exposure requires different safeguards. Many businesses focus on access controls but forget that shared files create their own, often permanent, risk.
Step 1: Clarify what the vendor needs
The safest way to reduce risk is to avoid sharing sensitive information from the start. Before signing any contract or granting system access, organizations should first classify the sensitive data involved to determine what can be shared with vendors and under what level of protection.
For example, a payroll provider may need employee names, bank details, and tax forms, but not performance reviews or internal HR notes. A marketing agency may need email addresses but not full customer profiles.
Ask the vendor to explain why each category of data is necessary and whether partial or masked information could work instead. A vendor who understands their process should be able to justify their request. If they cannot explain why they need certain data, that is usually a sign that the request is broader than necessary.
Step 2: Identify the sensitivity of the data
Not all business information carries the same level of risk. Some data can be shared with minimal concern, while other types require strict legal and technical protection.
You can group business data into the following categories:
1Public data — Information that is intended for public use and creates no risk if disclosed, such as website content, public pricing, or marketing materials.
2Internal data — Non-public information used inside the company that carries low risk if exposed, including internal schedules, planning notes, or organizational charts.
3Confidential data — Information that could harm the business if disclosed, such as contracts, customer lists, pricing strategies, or non-public financial details.
4Highly sensitive or regulated data — Data that requires the strongest controls due to legal or regulatory obligations, including personal identifiers, health information, financial account details, security credentials, and trade secrets.
Once you understand which category the data falls into, you can decide how much protection is required. This process, known as data classification, helps determine the appropriate level of protection before sharing information with vendors. The classification helps you take the next step — determining which legal documents you must have and whether additional privacy agreements are required before sharing the data.
Step 3: Use an NDA before sharing
A non-disclosure agreement is often the first formal safeguard in a vendor relationship. Without it, you may lose legal leverage if confidential information is misused or disclosed. In some cases, failing to use an NDA can even weaken trade secret protection under U.S. law.
Real court example: Electro-Craft Corp. v. Controlled Motion, Inc.
In Electro-Craft Corp. v. Controlled Motion, Inc., 332 N.W.2d 890 (Minn. 1983), the court refused to grant trade secret protection to certain technical information shared by the business.
One of the key reasons was that the company did not take reasonable steps to protect the information, including:
Failing to require written confidentiality agreements (NDAs);
Allowing broad access to sensitive information;
Relying on informal or verbal understandings of confidentiality.
The court held that trade secret protection depends not only on the value and secrecy of the information, but also on the owner’s efforts to keep it secret. Because Electro-Craft did not consistently use NDAs or other formal safeguards, the court concluded the information did not qualify as a protected trade secret.
The NDA should clearly describe:
What information is confidential, including specific categories such as customer data, pricing, security information, or proprietary materials.
How the information may be used, limiting use strictly to performing the agreed services.
Who may access the information, typically only individuals with a legitimate need to know.
How long the confidentiality obligation lasts, which is often 2–5 years, or longer for trade secrets.
What happens if the terms are violated, including available remedies such as injunctive relief and damages.
The key rule is simple: do not send sensitive files, screenshots, or system credentials BEFORE the NDA is signed.
If both sides are sharing sensitive information, a mutual NDA is usually appropriate. This type of agreement protects each party equally by placing the same confidentiality obligations on both sides. It ensures that information exchanged during discussions or collaboration cannot be disclosed or misused by either party.
Step 4: Controlling data use with service and vendor agreements
While an NDA sets confidentiality boundaries, it does not control how the vendor operates day to day. That role is handled by the service agreement and, in many cases, a separate vendor agreement. These are related, but different documents, and each plays a distinct role in managing data risk.
A service agreement focuses on the work itself. It explains what services the vendor will provide, how they may use your data to perform those services, and what security measures they must follow. It restricts data use to the service and confirms that all data and results belong to you.
A vendor agreement, by contrast, often governs the broader relationship. It may apply across multiple projects and sets baseline rules for compliance, security standards, breach response, liability, and termination. In longer or ongoing relationships, the vendor agreement is usually the primary document that controls how data is handled over time, even as individual services change.
Together, these agreements define security expectations such as access controls, encryption where appropriate, incident monitoring, and breach notification timelines. They also determine responsibility for data exposure and require the vendor’s cooperation in investigations and remediation.
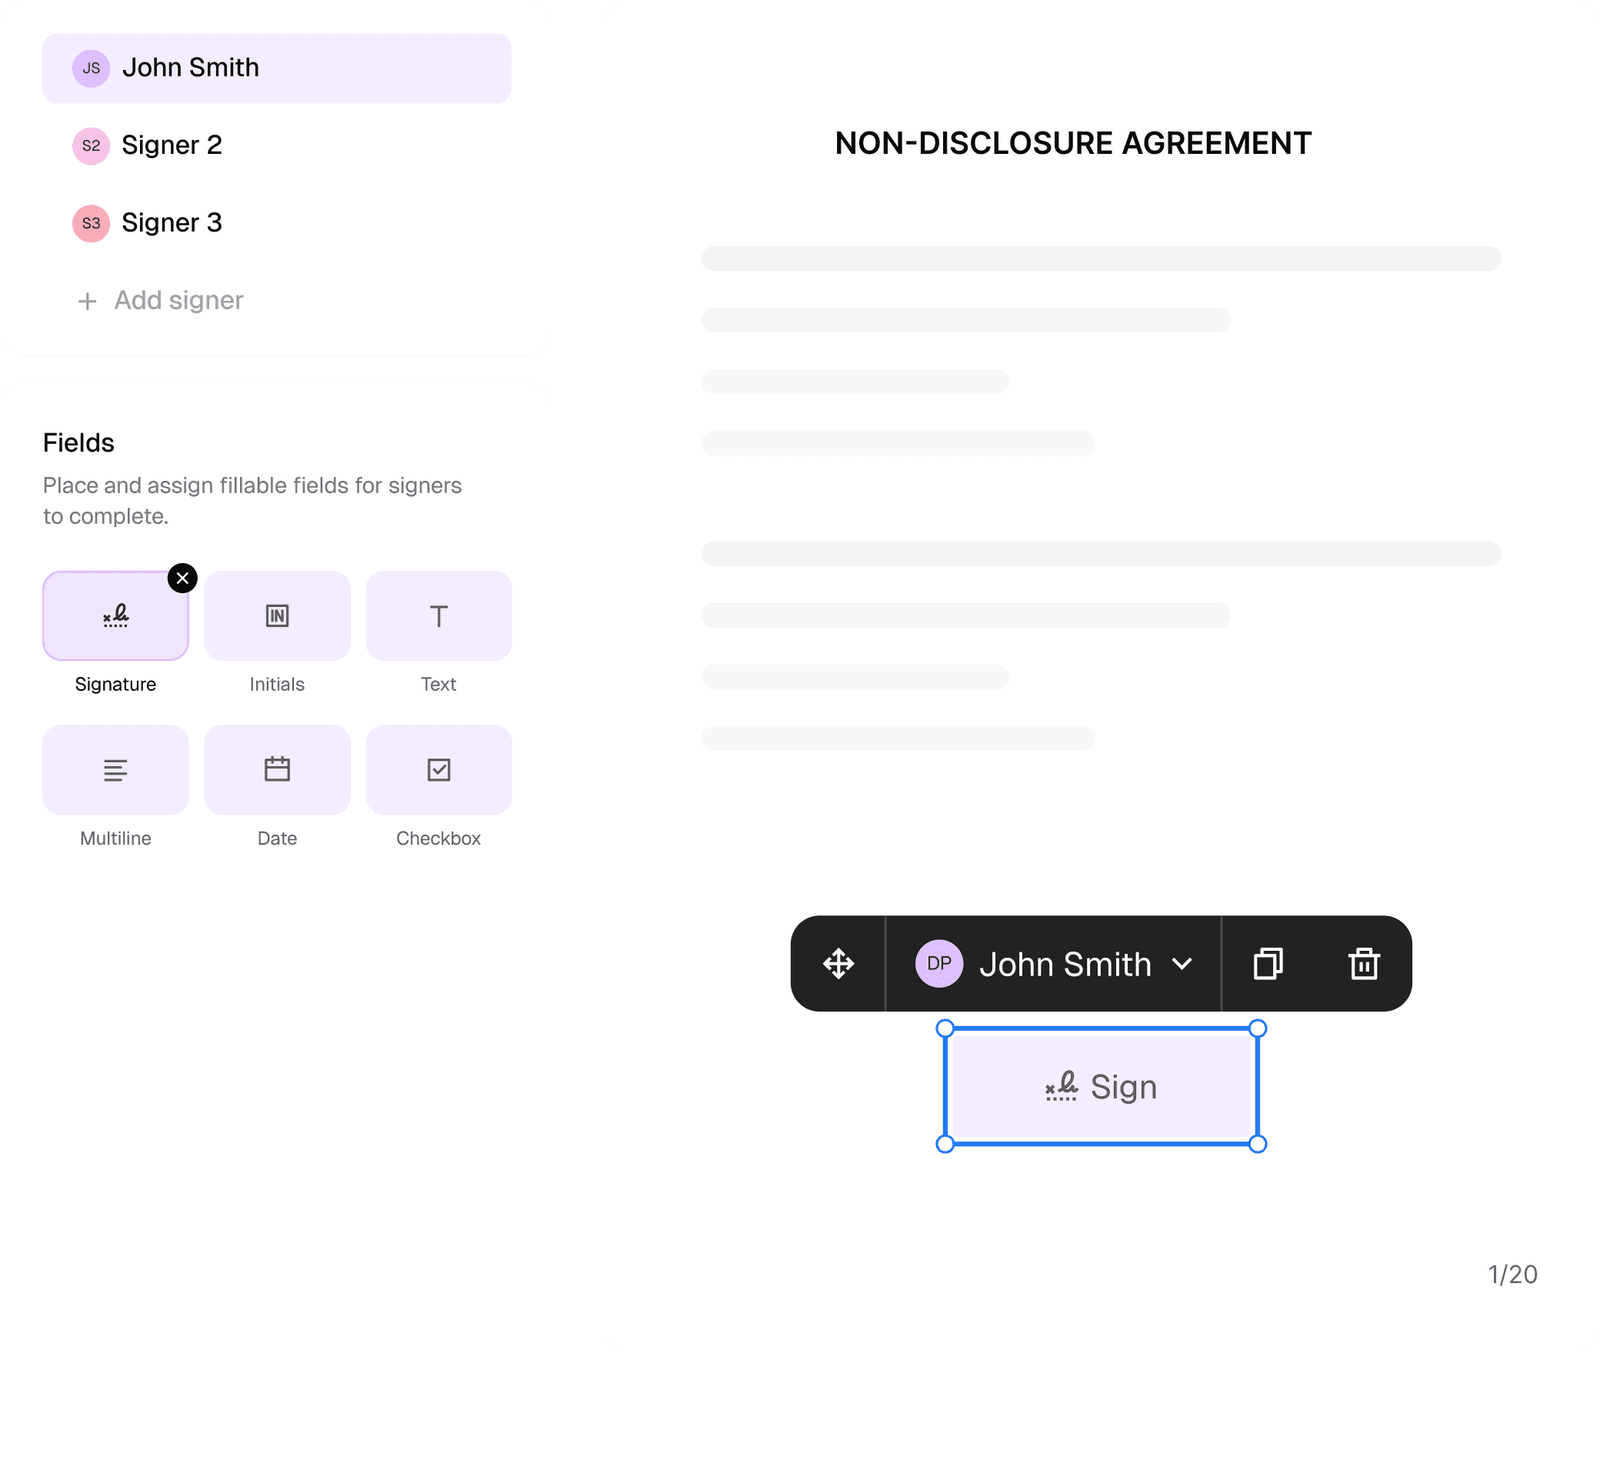
Once you’ve finished reviewing the agreements, signing them electronically is a reliable and legally valid option. Modern e-signature technologies protect documents on both the technical and legal levels by using identity verification, access controls, and tamper-evident audit trails.
Step 5: Choose secure sharing methods
How you share data is just as important as what you share. Email attachments and shared passwords often lead to accidental exposure, especially when files are forwarded or accounts are reused.
Industry reports show that 60% of data leaks occur due to employee mistakes or misuse of access, not technical failures. That’s why businesses should clearly instruct employees and vendors on how to handle data safely and use secure sharing methods.
So, what is the best way to share sensitive information? Below, we’ll take a broader look at secure data-sharing options and how to apply them in practice.
1Secure file portals allow you to share documents through expiring links with password protection or multi-factor authentication. They are useful for sending contracts, reports, and other sensitive files without permanently transferring control.
2Encrypted cloud storage with access controls lets you grant vendors access to specific folders rather than sending files individually. Permissions can be adjusted or revoked at any time, making this method suitable for ongoing collaboration.
3Individual, role-based system accounts should be used when vendors need to work directly inside your systems, such as CRMs or accounting platforms. Separate accounts allow you to limit permissions and track activity.
4VPN or secure network access adds an extra layer of protection when vendors need access to internal systems or infrastructure. This method helps restrict access to approved networks and devices.
This approach follows the principle of least privilege, meaning vendors receive only the minimum level of system access and data necessary to perform their tasks. Limiting permissions this way helps reduce the risk of accidental exposure or misuse of sensitive information. And when the working relationship ends, access should be removed just as carefully as it was granted.
If a vendor has been operating similarly to an internal team member, their access should be revoked using the same structured offboarding process used for employees — including disabling accounts, retrieving company assets, and confirming that all credentials and permissions have been properly removed. Following the same careful steps used when terminating an employee professionally helps ensure that no access points remain open after the collaboration ends.
Step 6: Monitor ongoing access
Even when it seems that all matters have been resolved, monitoring remains an equally important task. Vendor risk does not end after onboarding or contract signing.
Over time, vendors may change staff, update tools, or involve new subcontractors. Without regular review, access that was once appropriate can quietly become a security risk. Periodic checks help ensure that only authorized individuals still have access and that agreed security practices are being followed.
For higher-risk vendors, it is reasonable to conduct more formal reviews at least once a year. This may include confirming current access rights, reviewing security documentation, and checking the vendor’s readiness to respond to incidents.